One appliance turns what your estate reveals into finished remediation.
A private 120-billion-parameter model on its own GPU explains, extracts and drafts. It never decides.
0 gateways from the application network to the internet
Deterministic verdicts, with the model on or off
Every assessment ends the same way: a long list and a short team. ARTA turns the list into a programme, drafts the fix for each item, and holds every ticket until you have proof it is done.
120B
ParametersAn open-weight model held in memory on the appliance's own GPU. It never unloads on idle.
128GB
Unified memoryShared by CPU and GPU at 273 GB/s, so the model and the suite run side by side.
800+
Automated testsBehind ARTA-Fathom. The build fails if a write API or any network code appears in the scanner.
150+
AD indicatorsTen families in ARTA-Fathom, from Kerberos and Group Policy to certificate services and attack paths.
~40s
Remediation walkthroughA full walkthrough on a live ticket, drafted on the box.
0
Internet gatewaysThe application network has none. One proxy reaches one host: the sign-in provider's public keys.
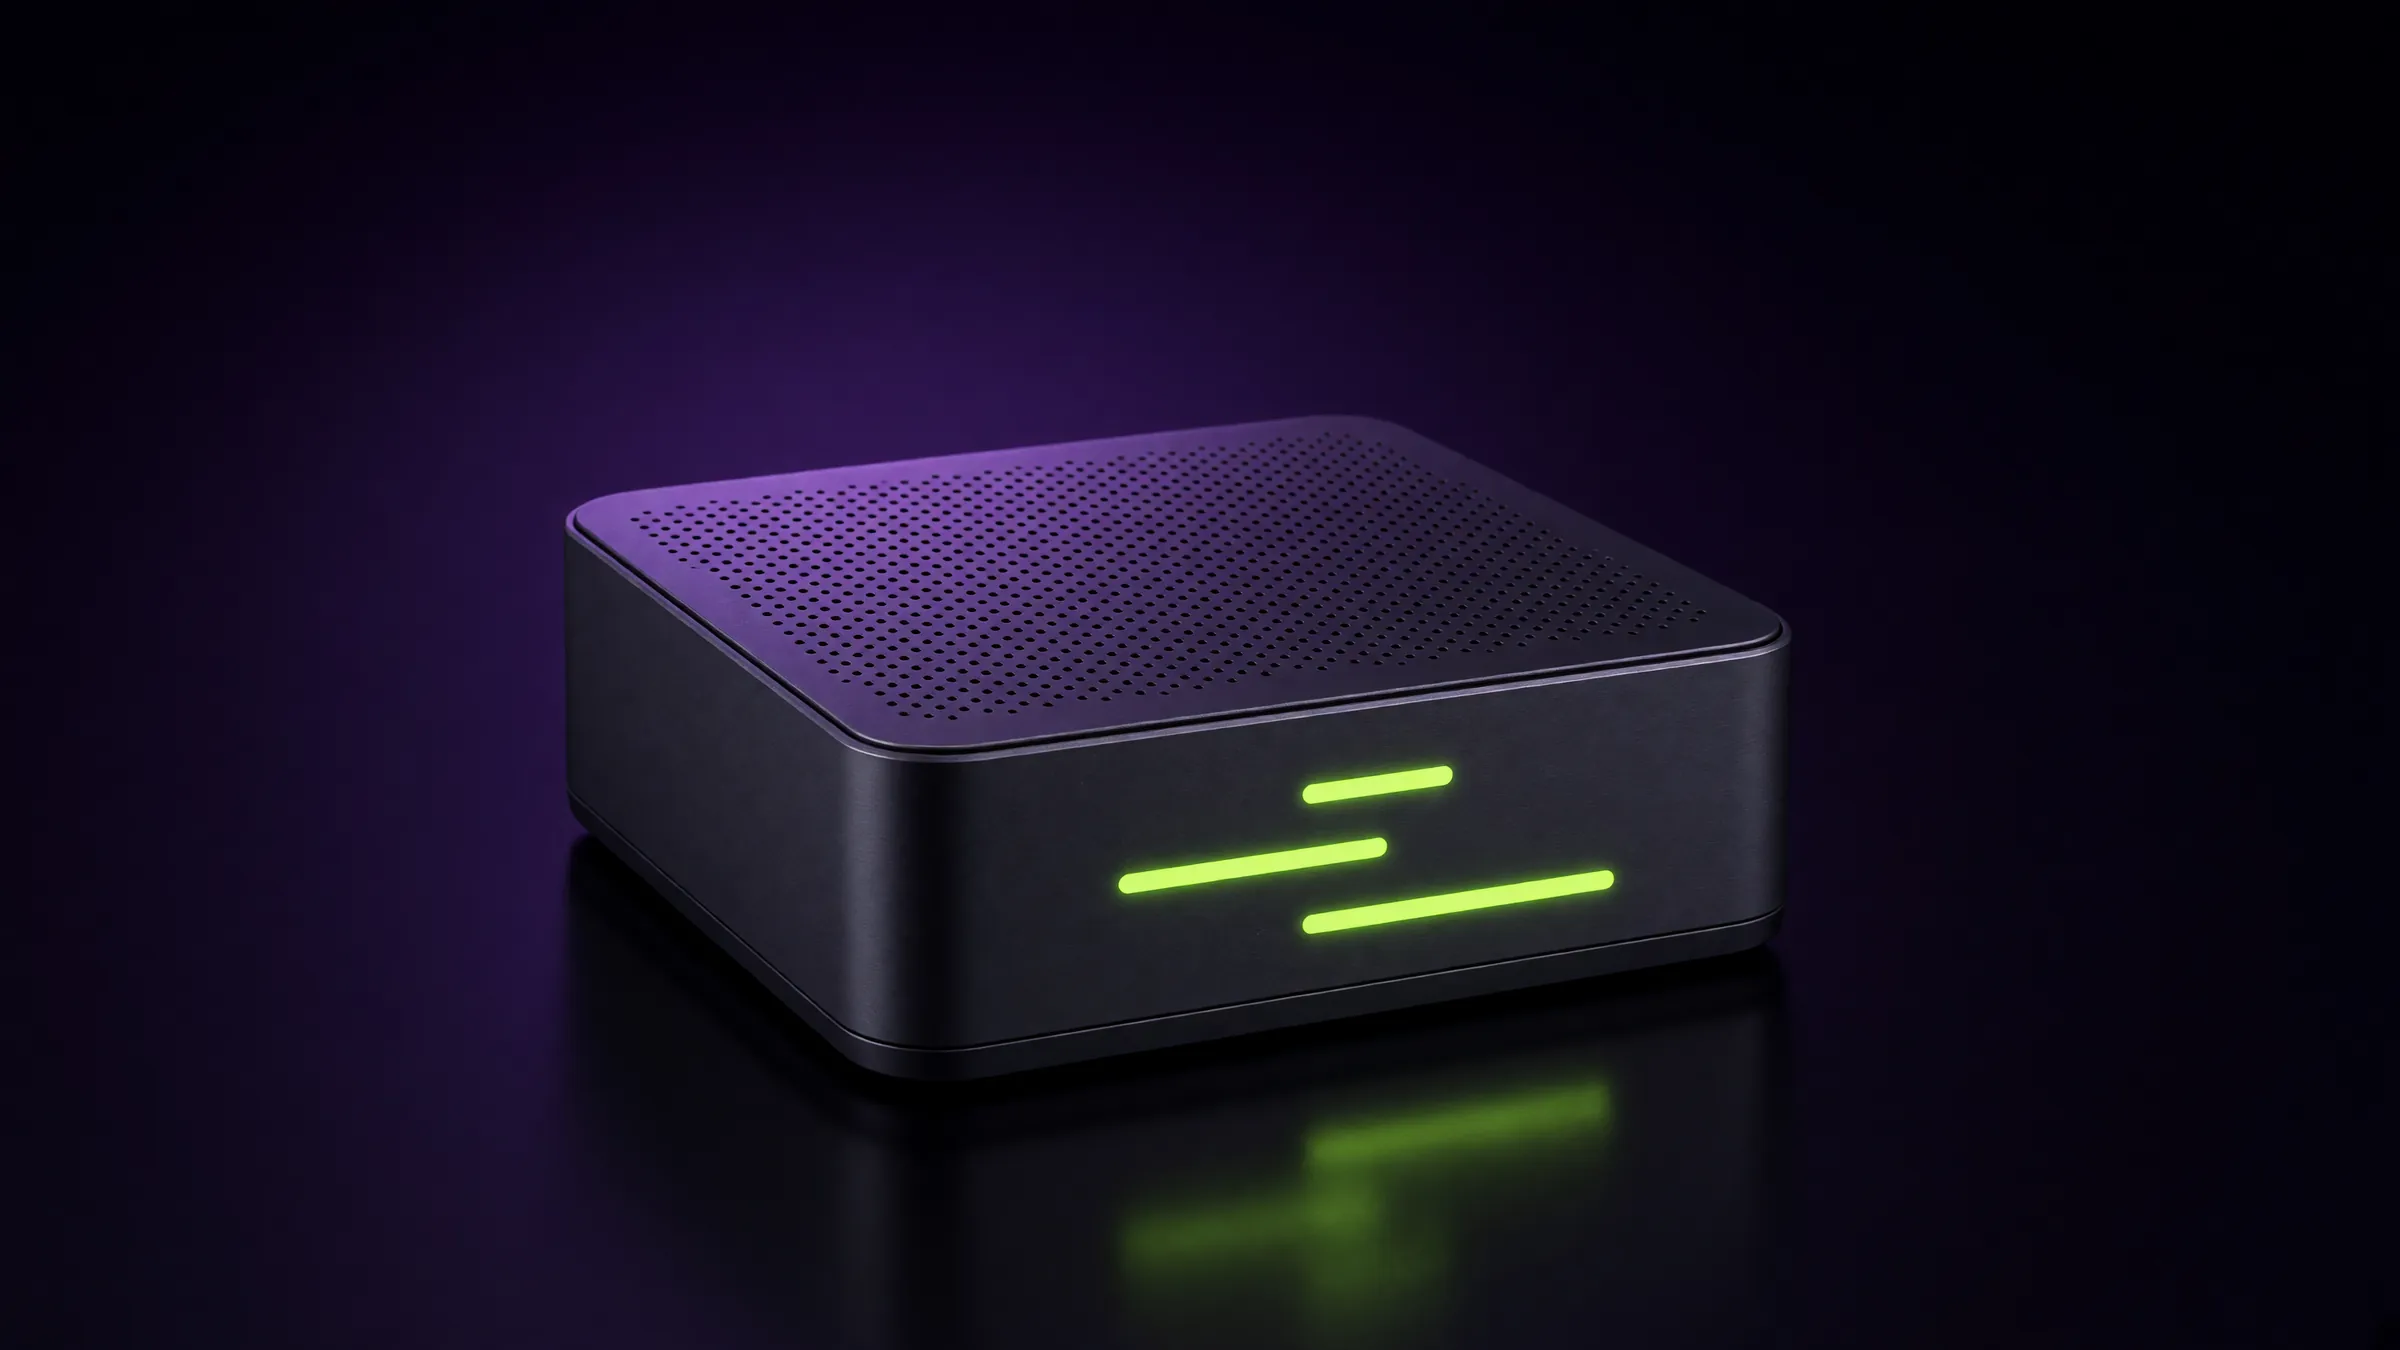
Render. Illustrative.
The appliance
A whole security suite in a box 150 mm square.
ARTA runs on a single Dell Pro Max with GB10. NVIDIA's Grace Blackwell superchip carries the model and every application in one machine with 128 GB of shared memory. Each application runs in its own container behind one reverse proxy, and each one updates or rolls back on its own.
Compute
NVIDIA GB10 Grace Blackwell Superchip20 CPU cores with an integrated Blackwell GPU
Memory
128 GB LPDDR5x unifiedShared by CPU and GPU, 273 GB/s
Storage
4 TB PCIe Gen 4 NVMeDatabases, documents and keys on a LUKS2 volume unlocked from the TPM
Network
10GbE RJ45Plus two 200Gb QSFP ports (NVIDIA ConnectX-7)
Ubuntu 24.04 LTS, ARM64Every application containerised and independently updatable
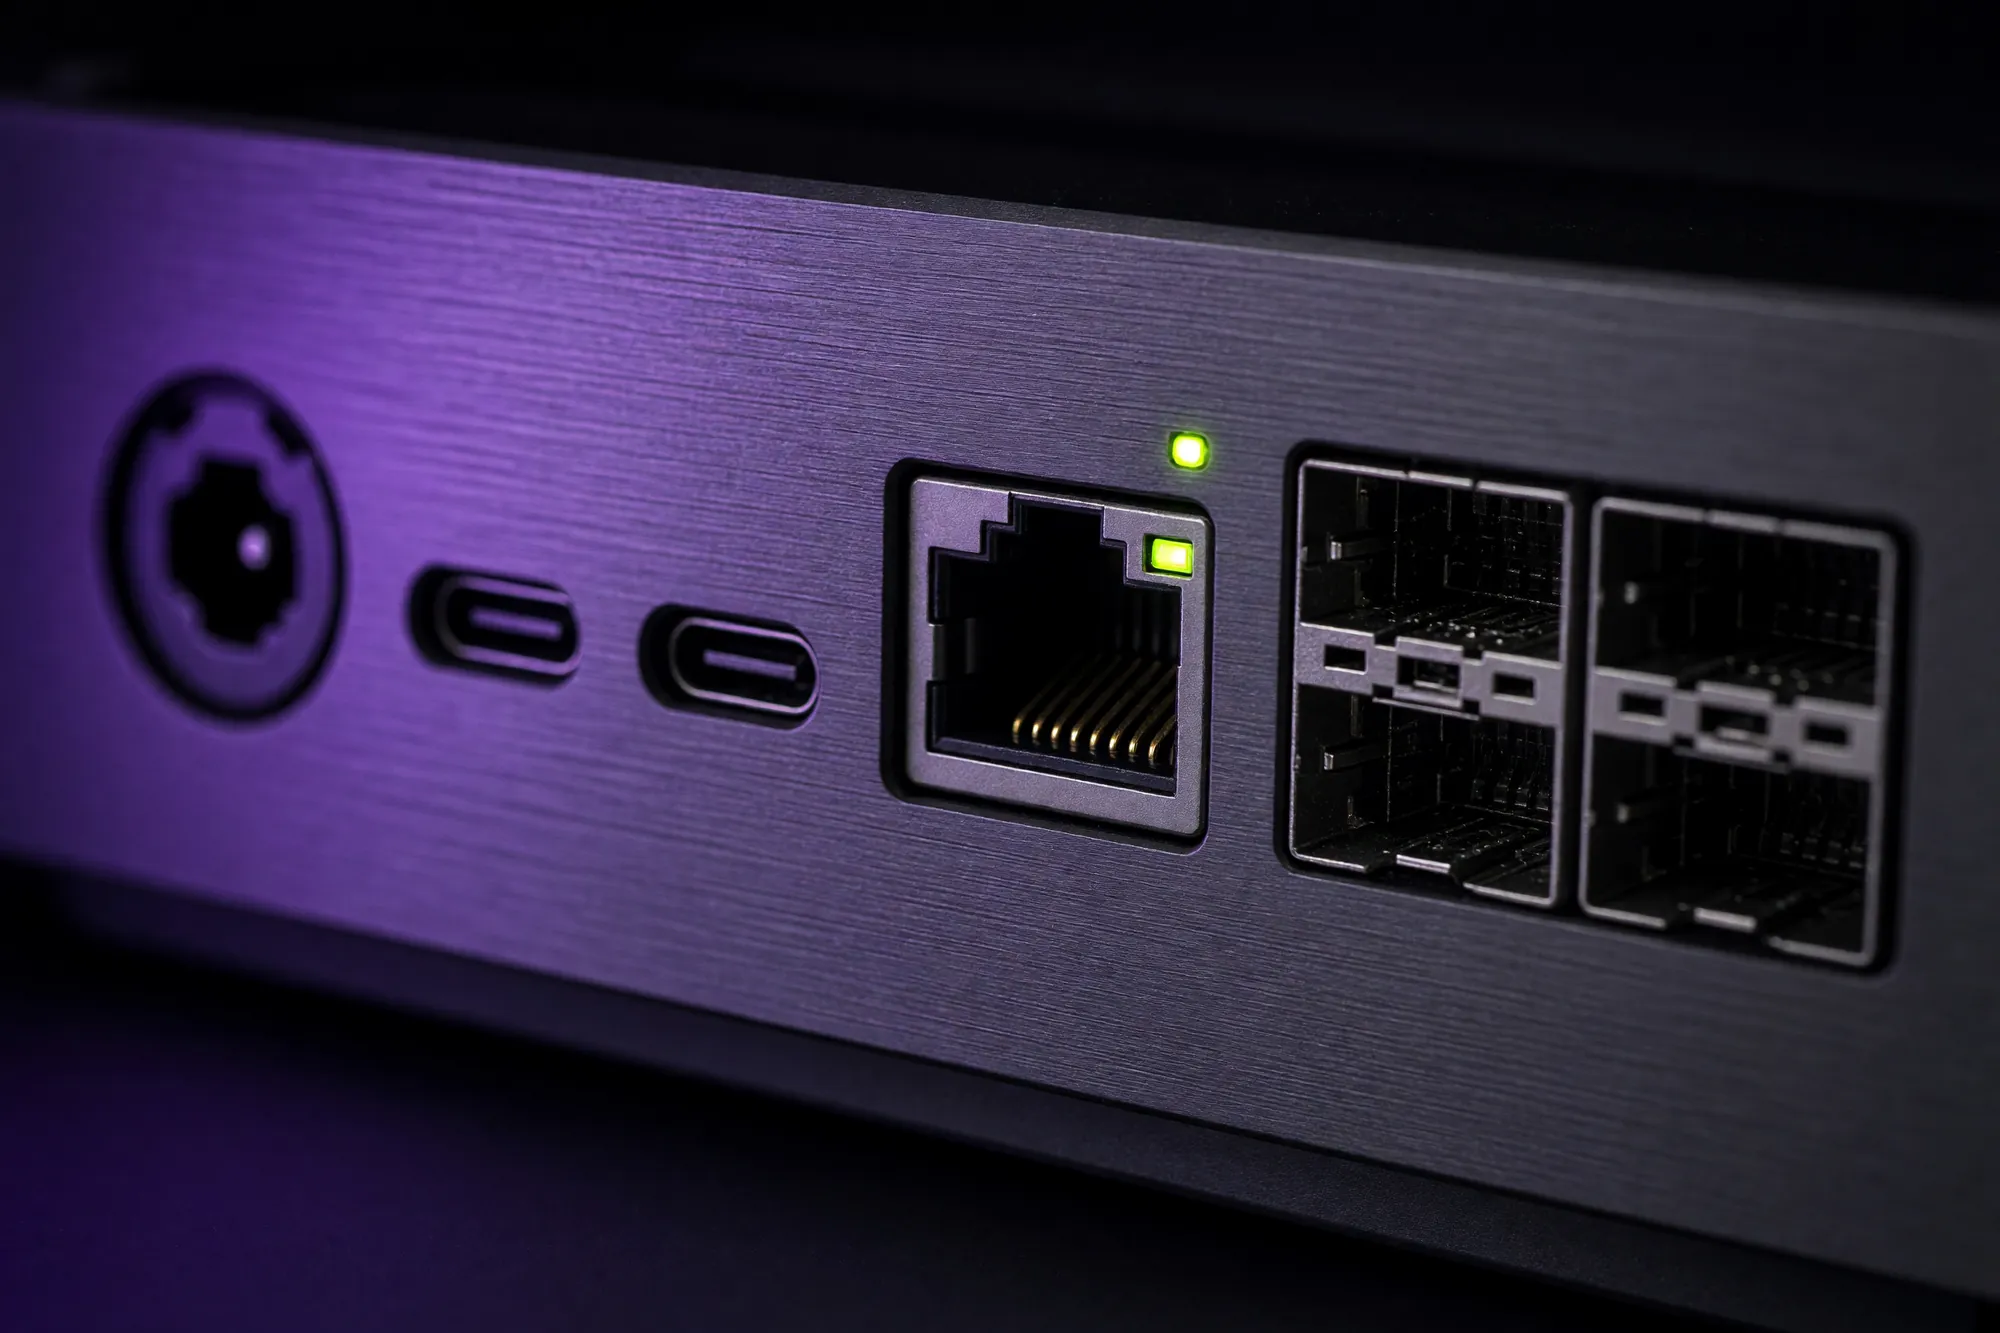
Rear panel
10GbE for the network, two 200Gb QSFP ports, one external supply.
The model
The model explains, extracts and drafts. It never decides.
gpt-oss:120b writes and nomic-embed-text indexes, both resident in memory and served from one container that owns the GPU. Deterministic code sets every verdict, score, severity, gate and SLA clock, and all of it works with the model switched off. We added the model for one job: shortening the gap between a finding appearing and an engineer knowing what to do.
No write access
It cannot move a ticket, change a setting, start a scan, clear a file or satisfy a proof gate.
Always warm
Held on the GPU at all times, with a 32k context. Answers never wait on a cold load.
Labelled as advice
Answers saved to a ticket carry the label "generated by the on-appliance model, not verified".
Reads what you collected
It works from the last collection, not the live estate, and stays as current as that collection.
Generated by the on-appliance model, not verifiedTimings compressed
What the model does in each application, and whether it can write anything
Application
What the model does
Can it write anything?
Tracker
Drafts remediation guidance on a ticket and answers read-only questions about the register.
No. It cannot move a ticket stage or satisfy the proof gate.
VScan
Triages every static-scan finding and drafts candidate fixes for the ones it judges exploitable.
Only into an isolated copy of the scanned code.
Redactor
On the opt-in full scan, reviews uncertain candidates and suggests keep or drop.
No. Export verification is deterministic and fails closed.
Gatekeeper
Nothing. Gatekeeper has no model and makes no AI calls of any kind.
Not applicable.
The suite
Eleven applications. One boundary.
Nine applications run on the appliance, behind one sign-in, on a network with no route to the internet. Two more, ARTA-Fathom and ARTA Courier, work inside your estate and send their results in.
Estate assessmentLive
Scope
The estate scanner and import point.
A read-only collector for AD, Group Policy, file shares, PKI, network, endpoints, Entra ID and Azure
Effective-policy and CIS Level 1 views, per OU
Pass, fail, not configured or not collected. Never a silent pass
Active DirectoryBuilt
ARTA-Fathom
An AD assessment run by an ordinary domain user.
150+ indicators across ten families, from Kerberos to attack paths
Resolves which Group Policy object wins, setting by setting
Read-only, no egress from the scanner, no exploitation. Enforced by build tests
Claims vs evidenceLive
Ledger
Checks what your documents claim against what the scan saw.
Reads the policies and designs you have written about yourself
Tests each claim against Scope's observations with 68 deterministic checks
Every verdict cites both the document and the evidence, re-checked hourly
Remediation programmeLive
Tracker
The programme, with a proof gate.
One ticket per check, with the affected items inside
SLA clocks per severity: 14, 30, 90 and 180 days
No ticket reaches a completed stage without proof
Source-code reviewLive
VScan
Static analysis with a triage pass and drafted fixes.
Semgrep across around twenty languages, plus PowerShell, Perl, VBScript, VBA, Batch and SQL
The model triages every finding and drafts fixes for exploitable ones
Drafts go to an isolated copy, get re-scanned, and never overwrite the original
Documents and screenshotsLive
Redactor
Redaction that checks its own work before export.
Twenty-four file types, with local OCR for text in screenshots
Remembers terms you confirmed for a client and catches them next time
Re-extracts every export and blocks it if anything survived
File intakeLive
Gatekeeper
The sheepdip in front of everything else.
ClamAV and YARA on every file in parallel, with adapters for more engines
Clean only when every running engine agrees. An engine error withholds the verdict
Hash-chained audit with a verifier in the app. Also a standalone Windows package
Document link agentBuilt
ARTA Courier
Seals documents inside your estate and sends them in.
A scheduled task on one Windows or Linux machine, reading only the shares or SharePoint sites you name
Each batch signed, encrypted and Merkle-rooted before it leaves
It cannot open a batch, even one it sealed
Plain-English questionsLive
Ask
Questions answered on the local model.
Ask about your estate in plain English
Read-only, grounded in what ARTA collected
Runs on the appliance's own GPU
Appliance healthLive
Caretaker
The watchdog that only ever reads.
Probes every application and the audit stores every fifteen minutes
Encrypted nightly backups the appliance cannot open
One logged action wipes an estate's data and keeps the audit chains
HomeLive
ARTAcore
The front door on the appliance.
Landing page and application launcher
Help and change log for every application
Live status and a resource monitor for the box
Automation
From first collection to proof of fix.
ARTA chains the work an engagement team does by hand. Collection feeds assessment, assessment feeds the programme, and the programme waits on evidence. People make the decisions. ARTA does the carrying.
01Collect
ScopeARTA-FathomARTA Courier
Collect
ARTA-Fathom reads Active Directory as an ordinary domain user. Scope's collector reads Group Policy, shares, PKI, network, endpoints, Entra ID and Azure. Courier seals the document folders you name, on a schedule.
Read-only, enforced in code and by build tests
Courier re-sends carry only the files that changed
02Admit
GatekeeperARTA Courier
Admit
Gatekeeper scans every incoming file with independent engines in parallel. Courier batches pass signature, Merkle root, chunk hash and decryption checks before ARTA writes a byte where an application can see it.
Verdicts fail closed. Forged batches refused early
Pushes land as raw bytes, with no parser at the boundary
03Assess
ScopeARTA-FathomVScan
Assess
Scope builds effective-policy and CIS Level 1 views for every OU. Fathom scores four pillars and reports domain risk as the worst of them, never the average.
New, resolved, regressed and unchanged between runs
Gaps reported as "not collected", never as a pass
04Reconcile
Ledger
Reconcile
Ledger extracts what your policies and standards claim, then checks each claim against what Scope observed. You see where the paperwork and the estate disagree.
Each verdict cites the document and the evidence
Documents re-checked every hour
05Prioritise
Tracker
Prioritise
Tracker turns findings into one ticket per check. Fifty accounts missing a second factor become one job, not fifty. SLA clocks start by severity.
Re-imports update the same tickets, no duplicates
Rows that disappear get flagged, never deleted
06Remediate
TrackerAskVScan
Remediate
On any ticket, the model drafts how to fix it, what could break, how to prove it and the commands, in about forty seconds. VScan drafts code fixes into an isolated copy and re-scans them.
Grounded in that ticket's own remediation steps
Copilot prompts built from an allow-list of fields
07Prove
Tracker
Prove
A ticket cannot enter a completed stage without a proof attachment. The server, the board and the detail page all enforce it. Blocked needs a written reason.
Three risk numbers, published side by side, never averaged
Manual target dates survive the next import
08Share
RedactorCaretaker
Share
Redactor strips client detail from evidence and reports, then re-reads every export to confirm it worked. Caretaker backs everything up nightly, encrypted to a key held off the box.
Export blocked if any accepted entity survives
Overrides recorded and marked "exported unverified"
Touch points
Where ARTA meets your estate.
Every collector reads, and nothing writes back. Pick a system to see what ARTA touches, how it gets there, and which way the data moves.
Appliance
Read-only
Active Directory
Apps
Access
Direction
Writes back
Data flowing into ARTAOutbound: a key request, and prompts you paste
Deployment
Two ways in. Same boundary.
Put the appliance inside your network, or keep your network as it is and open only the applications your remediation needs. The suite, the model and the guarantees stay the same.
Method 1
Internally situated
The appliance on your network, in your comms room, under your control.
The same appliance, racked in your building. ARTA-Fathom and ARTA Courier already run inside your estate; with the appliance beside them, their results reach it without crossing the internet. Collection, analysis, the model and the records all sit within your walls.
Collected where it lives. Read-only collectors hand their results straight to the box on your own network.
Updates you can carry in. Gatekeeper's signatures arrive as an offline bundle with a checksum manifest, verified before install.
Keys that stay with the box. A TPM-bound encrypted volume, and backups only a key held elsewhere can open.
Handed back clean. One logged action wipes your data and keeps logins, configuration and audit chains.
Method 2
Gated app access
Open only the applications your remediation needs.
onionio hosts and operates the appliance in the UK. You open the applications the work requires, such as Tracker for the programme, Ask for answers and Redactor for evidence, and pay down tech debt without a new box in your rack.
Published app by app. Each application has its own address behind Cloudflare Access, reached through an outbound-only tunnel. The appliance opens no inbound ports.
Entra ID, then checked again. Each application verifies the signed sign-in token itself: signature, issuer, expiry and audience. Roles are set per application.
Pushed, never pulled. fathom-connect sends a signed export after you confirm it. Courier batches cross the wire as ciphertext. ARTA never reaches into your network.
Break-glass that announces itself. Local logins cover an identity-provider outage, and every successful one raises a critical finding.
The two deployment methods compared
Inside your estate
Gated app access
Where it runs
Your comms room, on your network
An onionio-operated appliance in the UK
How data arrives
Collectors and Courier hand results over inside your network
Signed exports and sealed batches, pushed out from your side
What people reach
The suite, on your network
Only the applications you open, each at its own address
Sign-in
Single sign-on, with break-glass local accounts
Entra ID through Cloudflare Access, verified again by each application
Internet from the apps
No gateway on the application network
No gateway; one proxy fetches the sign-in keys
Suits
Estates that keep data inside their own walls
Teams that want the outcome without new hardware
Sovereignty
Private by construction, not by policy.
Six mechanisms run on the appliance today. Each one is a property of the machine that you can inspect.
01
No route out for the applications
The application network has no internet gateway. A single proxy permits one host, the sign-in provider's public-key endpoint, so each application can verify signed tokens.
02
Encrypted at rest, unlocked by the machine
Documents, databases, keys and configuration sit on a LUKS2 volume bound to the TPM and platform state. Swap takes a fresh key at every boot.
03
Backups the appliance cannot open
ARTA encrypts nightly backups to a public key. Only a private key held off the box opens them. Volume recovery material lives off the machine too.
04
Break-glass that announces itself
Entra ID single sign-on at the edge, checked again by each application. Local password logins keep the suite alive in an outage, and each use raises a critical finding.
05
A watchdog that only ever reads
Every fifteen minutes Caretaker probes each application and runs read-only rules over the audit stores: sign-in spikes, locked accounts, break-glass use, the model's place on the GPU.
06
Handed over clean
One administrator action wipes every application's customer data and keeps logins, configuration and audit chains. It needs a typed confirmation, and ARTA logs every run.
Silence is never presented as safety.
CIS Controls v8CIS BenchmarksNCSC CAFCyber EssentialsNHS DTACMappings, not certification
Plainly
What ARTA isn't.
ARTA works from what you have collected. It sits beside your monitoring and response, and leaves those jobs to the tools built for them.
A live monitor. It does not watch your estate for attacks in progress.
An incident responder. It does not contain, eradicate or recover.
A threat-intelligence feed. It carries none, and it has no route to fetch one.
A penetration test. Fathom reports an attack path. It never walks one.
A decision-maker. The model drafts. Your engineers decide, and Tracker holds them to proof.
Clear the list. Keep the proof.
Talk to onionio about putting ARTA to work on your estate, inside your walls or through gated access.